Shadow AI in Small Businesses: How to Find Unapproved Tools and Agents
Affiliate Disclosure: We review products independently. When you buy through our links, we may earn a commission or a compound recurring commission at zero extra cost to you. Read our editorial policy.
Small businesses are adopting artificial intelligence faster than many can establish rules for using it. Employees are experimenting with AI assistants, connecting apps through automation platforms, and building workflows that move information between business systems. These activities can improve productivity, but they can also introduce costs, security risks, and processes that management does not know exist.
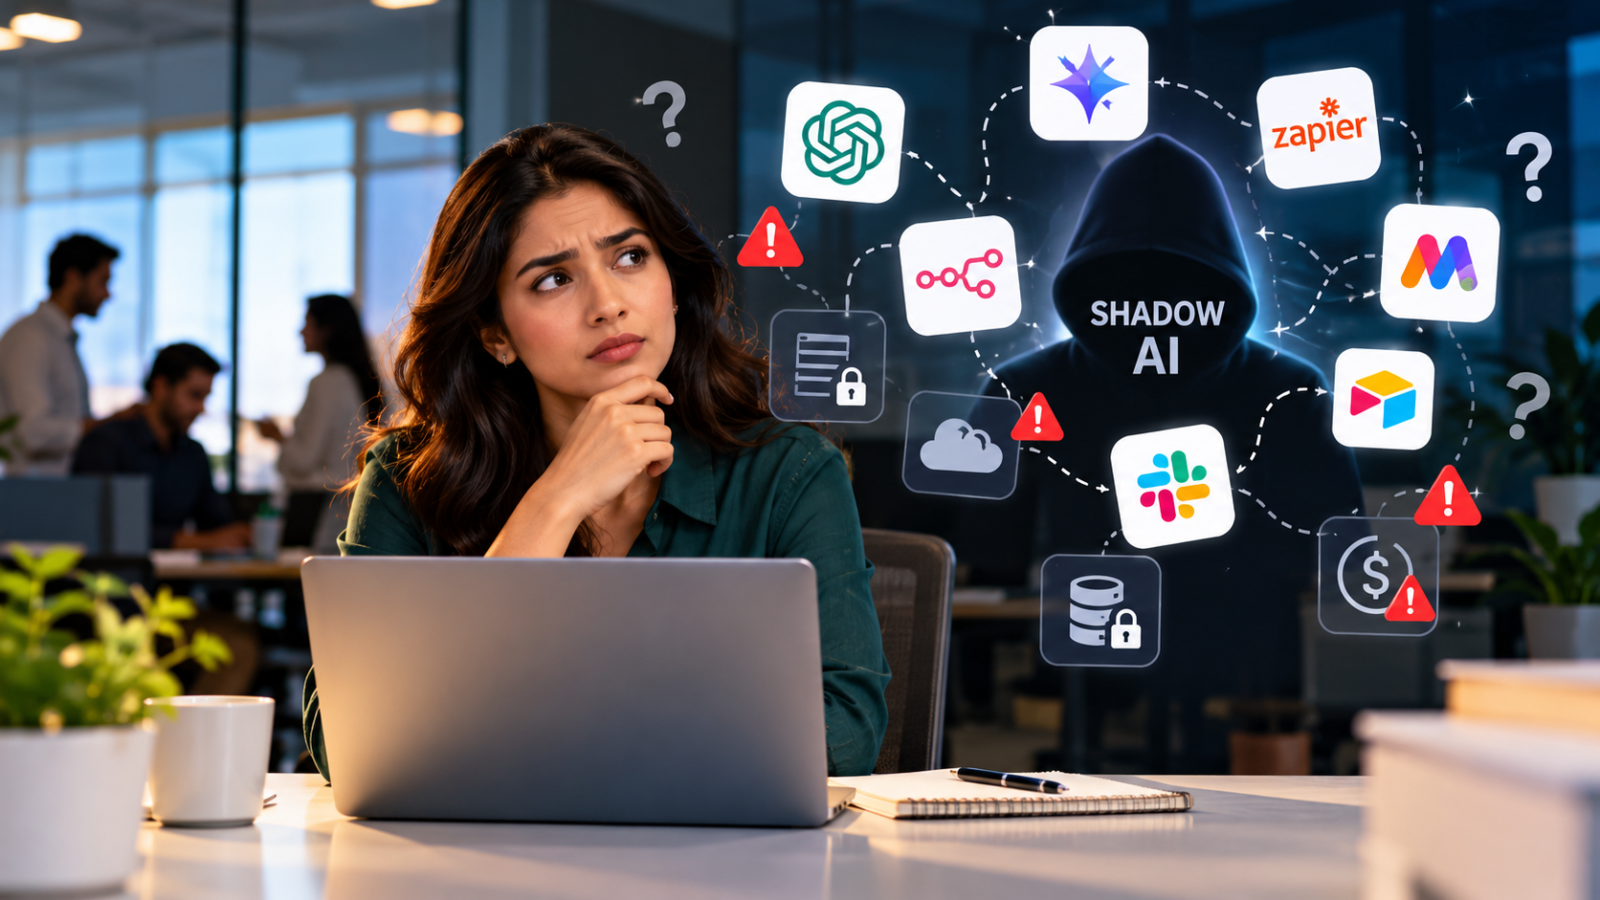
This is the growing challenge of shadow AI: AI tools, integrations, and automated workflows operating without appropriate organizational approval or oversight.
The issue is no longer limited to employees using a free chatbot for writing emails. AI can now be embedded in customer relationship management systems, spreadsheet workflows, meeting assistants, customer support platforms, and multi-step agents that take actions on a user’s behalf.
A report released by Pax8 on October 12, 2026, highlights the scale of the governance challenge. Among AI-engaged small and midsize businesses surveyed, 35% had discovered unapproved tools, workflows, or agents operating in their organizations during the previous six months. The report also found that 49% of businesses that paid for AI in the preceding year had received at least one higher-than-expected bill or usage charge.
These findings do not mean that every unapproved tool is dangerous. They do show why businesses need visibility into how AI is being used, what systems it can access, and what it costs.
What Is Shadow AI?
Shadow AI refers to AI applications, services, integrations, or agents used within a business without the knowledge or approval of the people responsible for managing technology, security, compliance, or spending.
It can appear in several forms:
- Unapproved AI assistants: Employees use personal or free accounts to summarize documents, draft proposals, analyze customer information, or write code.
- AI features inside existing software: Staff activate AI capabilities in applications without checking the organization’s data policies or subscription terms.
- Untracked workflow automations: Someone connects an AI model to email, spreadsheets, a CRM, or a project management platform using an automation tool.
- Unofficial AI agents: An employee builds an agent that searches records, updates applications, sends messages, or performs multiple tasks without a formal review.
- Unmanaged API usage: A developer or consultant connects an AI provider’s API to a business process without a documented owner, budget, or monitoring plan.
The important distinction is not simply whether management approved a particular AI brand. It is whether the business understands the tool’s purpose, data access, permissions, cost, and accountability.
An employee using an approved writing assistant to draft a generic social media post presents a different risk from an unreviewed agent with access to customer records and the ability to send external emails.
Why Shadow AI Is Becoming Harder to Manage
1. AI is spreading across the software stack
Businesses no longer encounter AI only through standalone chat applications. AI features can appear in email platforms, CRM systems, collaboration tools, analytics products, customer service software, and automation platforms.
A business may approve a core application without realizing that employees have enabled additional AI features or connected third-party services to it.
This makes a simple list of purchased software insufficient. Businesses also need to understand which AI capabilities are active and what information those capabilities can access.
2. No-code automation makes experimentation easy
Platforms such as Zapier, Make, and n8n allow users to connect applications without building every integration from scratch. When combined with AI models, these tools can support workflows that classify incoming requests, summarize documents, enrich lead records, draft responses, or route tasks to the appropriate team.
The benefit is speed. The risk is that an employee can create a useful workflow before anyone has reviewed its permissions, error handling, or long-term ownership.
A workflow that starts as a small experiment may become part of daily operations. If its creator leaves the company, changes an account, or reaches a usage limit, the business may struggle to understand or maintain it.
3. AI usage can create unexpected costs
Some AI services charge through subscriptions, while others use consumption-based billing. Costs may depend on model usage, API requests, tokens, workflow executions, connected applications, or additional usage beyond a plan allowance.
A single low-cost experiment may not attract attention. Several workflows running repeatedly across business systems can create a much larger bill.
Pax8’s October 2026 findings indicate that unexpected AI charges are a real budgeting concern among the businesses it surveyed. The practical response is to assign an owner to every business-critical AI workflow and monitor its actual usage rather than relying solely on the advertised starting price.
4. Data access can expand beyond the original task
An AI tool may need access to files, messages, customer records, or internal documents to perform its intended function. An automation can also pass information from one application to another.
If permissions are broader than necessary, a tool may be able to retrieve or modify information unrelated to its task. Sensitive information entered into an external service may also be subject to that provider’s data handling, retention, and privacy terms.
The Australian Cyber Security Centre’s guidance for small businesses identifies data leakage, privacy breaches, unreliable outputs, and supply chain vulnerabilities among the risks associated with AI adoption. These concerns apply even when the original intention is simply to save employees time.
How to Find Shadow AI in Your Business
A small business does not need an enterprise security department to begin. It needs a structured inventory and a clear process for reviewing what it finds.
Step 1: Create an inventory of AI tools and workflows
Start with a short questionnaire for employees and contractors. Ask which AI tools they use, what work they perform with them, and whether those tools connect to business applications.
Include standalone assistants, AI features embedded in software, browser extensions, automation platforms, custom API integrations, and agents built for internal use.
Then compare the responses with the software subscriptions and integrations already known to the business.
Where appropriate, review available application logs, identity management records, connected-app permissions, and vendor administration consoles. Do not assume that one source will reveal every tool.
Step 2: Map the data each tool can access
For every identified tool or workflow, record the types of information it handles.
| Data category | Examples | Suggested approach |
|---|---|---|
| Public information | Published articles, public product descriptions | Generally lower risk, subject to company policy |
| Internal business information | Internal procedures, nonpublic plans, routine operational documents | Review the vendor’s data handling and access controls |
| Customer or employee information | Contact details, support records, employee files | Require explicit approval and appropriate safeguards |
| Sensitive business information | Financial records, credentials, confidential contracts, regulated data | Restrict access and require a formal security and privacy review |
This is a practical starting point, not a universal legal classification. Businesses should adapt it to their industry, contractual obligations, and applicable privacy requirements.
Step 3: Review integrations and permissions
A tool’s risk depends partly on what it can do.
An AI assistant that generates a draft without external access has a different risk profile from an agent that can read a shared inbox, modify CRM records, and send messages to customers.
For each connected application, check:
- Which accounts and records can the integration access?
- Can it only read data, or can it also create, update, or delete records?
- Can it send messages or trigger financial or operational actions?
- Who authorized the connection?
- Can the business revoke access quickly if something goes wrong?
Grant only the permissions required for the intended task. For higher-impact actions, use approval steps rather than giving an agent unrestricted authority.
Once you identify unapproved AI tools and workflows, review their access permissions, connected credentials, and security settings using this AI automation security checklist.
Step 4: Review actual usage and costs
Check subscription invoices, API dashboards, automation execution histories, and usage reports where available.
Look for unexpected increases, duplicated workflows, unused subscriptions, repeated AI calls, and automations that continue running after the original project has ended.
Set spending alerts where the provider supports them. For important workflows, document the expected monthly volume and define a process for investigating unusual usage.
A cost review should distinguish between the base subscription, usage charges, additional integrations, and the time required to maintain the workflow.
Step 5: Assign an owner to every important workflow
Every business-critical automation should have a named owner who understands its purpose and knows how to maintain it.
Document the trigger, connected applications, data handled, expected output, failure behavior, and process for disabling the workflow. Record any external dependencies and the account used to operate it.
If a workflow has no owner, no documentation, and no clear business purpose, review whether it should be transferred to an approved owner or retired.
Build a Simple AI Approval Process
Banning every unapproved AI tool may seem like the easiest response, but it can discourage employees from disclosing useful experiments. A practical policy should make it clear how employees can request approval and what information they need to provide.
Use a lightweight review process with three levels.
Level 1: Low-risk experimentation
Examples include drafting generic marketing copy, brainstorming ideas, or summarizing public information using an approved tool.
Employees should follow the organization’s standard AI policy and avoid entering confidential or personal information unless the tool is approved for that purpose.
Level 2: Business workflow integration
Examples include connecting an AI model to a CRM, processing support tickets, analyzing internal documents, or automating routine email workflows.
Require a documented business owner, a review of data handling, appropriate permissions, basic testing, and a way to monitor errors and usage costs.
Level 3: High-impact or autonomous actions
Examples include agents that can modify important records, send external communications without review, make consequential recommendations, or initiate financial or operational actions.
Require a more formal review, limited permissions, testing of failure scenarios, monitoring, and human approval for consequential actions where appropriate.
This tiered approach keeps routine experimentation manageable while giving higher-risk workflows additional oversight.
A 30-Day Plan for Small Businesses
Businesses that have never inventoried their AI use can start with a short, time-bound review.
Week 1: Discover. Ask employees about their AI tools and workflows. Review known software subscriptions and connected applications.
Week 2: Assess. Identify tools handling sensitive data, workflows with broad permissions, unexpected usage charges, and automations without owners.
Week 3: Control. Approve appropriate tools, remove unnecessary permissions, assign owners, and establish spending alerts where available.
Week 4: Document. Publish a simple AI usage policy, create an approval route for new tools, and schedule periodic reviews of critical workflows.
The goal is not to eliminate every risk in 30 days. It is to establish visibility and accountability so the business can make informed decisions about AI adoption.
How to Measure Whether Your AI Governance Is Working
A policy is only useful if the business can tell whether it is being followed. Track a small number of practical indicators:
- Percentage of business-critical AI workflows with a named owner.
- Percentage of identified AI tools reviewed and approved.
- Number of workflows with documented data access and permissions.
- Monthly AI and automation spending compared with the budget.
- Number of unresolved high-risk findings.
- Time required to disable an unapproved or malfunctioning integration.
These measures should support better decisions, not create unnecessary administration. A five-person company may need only a spreadsheet and a monthly review. A larger organization with sensitive customer data or complex integrations may need dedicated security and governance tools.
Final Takeaway: Make AI Visible Before Scaling It
Shadow AI is not necessarily evidence of employee misconduct. It often reflects a gap between the speed of experimentation and the organization’s ability to review new technology.
For small businesses, the best response is to identify the tools already in use, understand what information they access, review their permissions, monitor their costs, and assign clear ownership to important workflows.
AI agents and automation platforms can deliver meaningful operational benefits. Those benefits are easier to sustain when the business can see what is running, explain why it is running, and intervene when it behaves unexpectedly.
Start with visibility, apply controls in proportion to risk, and give employees a clear way to bring useful AI experiments into the approved software stack.